
Shadowing Practice: MITRE ATT&CK® Framework - Learn English Speaking with Video
 C1
7 Phases of Penetration Testing Explained | Think your system is safe? #cybersecurity #pentesting
 C1
The Data-Driven Decision Framework Every Marketer Needs
 C1
Google Threat Intelligence Platform Overview
 C1
Master n8n Triggers in 20 Minutes – Automate Anything
 C1
Trust the Process: How to Design Teams That Actually Work
 C1
How I Made $30,000 Hacking Broken Access Control
 C1
Executing Monitoring, Evaluation and Learning (MEAL) | Complete Practical Guide
 C1
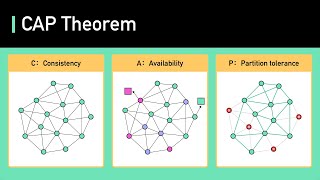
CAP Theorem Simplified
 C1
Terraform Scenario Based Interview Questions and Answers | DevOps Interview
 B2
Retired Navy SEAL Explains How to Prepare for Dangerous Situations | Tradecraft | WIRED
 C1
Course Preview | SC-100 | Microsoft Cybersecurity Architect
 B2
🔥They Studied Your Weaknesses
Woordenschat en spreektips bij deze les
Deze video bevat 34 zinnen en 490 woorden om na te spreken. Het gesproken deel duurt 3:35. De spreker praat in een gelijkmatig tempo van ongeveer 137 woorden per minuut, prettig om te shadowen. Slechts 74% van de woorden hoort bij de 3.000 meest gebruikte Engelse woorden, dus de woordenschat is pittig.
Belangrijke woorden in deze video
15 woorden uit de video die het leren waard zijn, met uitspraak en betekenis:
| Woord | Uitspraak | Betekenis |
|---|---|---|
| technique zelfstandig naamwoord | /tɛkˈniːk/ | techniek |
| framework zelfstandig naamwoord | /ˈfɹeɪm.wɜːk/ | geraamte |
| detect werkwoord | /dɪˈtɛkt/ | detecteren |
| objective zelfstandig naamwoord | /ɒbˈd͡ʒɛk.tɪv/ | object |
| define werkwoord | /dɪˈfaɪn/ | bepalen, determineren |
| domain zelfstandig naamwoord | /ˌdəʊˈmeɪ̯n/ | domein |
| tactics zelfstandig naamwoord | /ˈtæktɪks/ | tactiek |
| tactic zelfstandig naamwoord | /ˈtæktɪk/ | tactiek, gevechtsleer |
| select werkwoord | /sɪˈlɛkt/ | uitkiezen, selecteer |
| solve werkwoord | /sɒlv/ | oplossen |
| resource zelfstandig naamwoord | /ɹɪˈzɔːs/ | bron, hulpbron |
| enterprise zelfstandig naamwoord | /ˈɛntəˌpɹaɪz/ | onderneming |
| collect werkwoord | /ˈkɑlɪkt/ | verzamelen, opstapelen |
| extend werkwoord | /ɛkˈstɛnd/ | uitbreiden |
| privilege zelfstandig naamwoord | /ˈpɹɪv.(ɪ.)lɪd͡ʒ/ | voorrecht, privilege |
Uitspraak om op te letten
- De klanken “sh” en “zh”: observation /ˌɑbzɚˈveɪʃn̩/, evasion /ɪˈveɪʒən/
- Lange woorden — let op de klemtoon: availability /əˌveɪ.ləˈbɪl.ɪ.ti/, analytics /ˌæn.əˈlɪt.ɪks/, adversary /ˈæd.vəɹˌsɛɹi/, laterally /ˈlæ.tə.ɹə.li/
Zo oefen je met deze video
- Luister de hele video één keer zonder te spreken en noteer de woorden die je niet kent.
- Spreek zin voor zin na op normale snelheid en herhaal elke zin tot je ritme gelijk is aan dat van de spreker.
- Neem jezelf op en vergelijk met het origineel; let daarbij op woorden als technique, framework, detect.
Wat is de Shadowing-techniek?
Shadowing is een wetenschappelijk onderbouwde taalleermethode die oorspronkelijk is ontwikkeld voor professionele tolkentraining en gepopulariseerd door polyglot Dr. Alexander Arguelles. De methode is eenvoudig maar krachtig: je luistert naar native Engelse audio en herhaalt het onmiddellijk hardop — als een schaduw die de spreker volgt met slechts 1–2 seconden vertraging. In tegenstelling tot passief luisteren of grammaticadrills, dwingt shadowing je hersenen en mondspieren om echte spraakpatronen tegelijkertijd te verwerken en te reproduceren. Onderzoek toont aan dat het de uitspraaknauwkeurigheid, intonatie, ritme, verbonden spraak, luisterbegrip en spreekvaardigheid aanzienlijk verbetert — waardoor het een van de meest effectieve methoden is voor IELTS Speaking-voorbereiding en echte Engelse communicatie.