
Pratica di Shadowing: MITRE ATT&CK® Framework - Impara a parlare inglese con i video
 C1
7 Phases of Penetration Testing Explained | Think your system is safe? #cybersecurity #pentesting
 C1
The Data-Driven Decision Framework Every Marketer Needs
 C1
Google Threat Intelligence Platform Overview
 C1
Master n8n Triggers in 20 Minutes – Automate Anything
 C1
Trust the Process: How to Design Teams That Actually Work
 C1
How I Made $30,000 Hacking Broken Access Control
 C1
Executing Monitoring, Evaluation and Learning (MEAL) | Complete Practical Guide
 C1
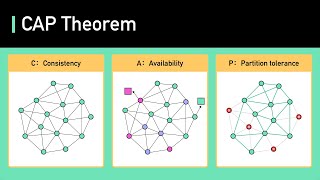
CAP Theorem Simplified
 C1
Terraform Scenario Based Interview Questions and Answers | DevOps Interview
 B2
Retired Navy SEAL Explains How to Prepare for Dangerous Situations | Tradecraft | WIRED
 C1
Course Preview | SC-100 | Microsoft Cybersecurity Architect
 B2
🔥They Studied Your Weaknesses
Informazioni sulla lezione
In questa lezione, praticherai l'ascolto e la ripetizione di un video tecnico sull'ATT&CK Framework di MITRE, un argomento cruciale nella cybersecurity. Imparerai a seguire un discorso strutturato, comprendere termini specifici e migliorare la tua pronuncia inglese. La lezione si concentra sulla tecnica del "shadowspeak", che aiuta a sincronizzare la tua voce con il ritmo e l'intonazione del parlante, fondamentale per una conversazione fluida in inglese.
Parole chiave e frasi utili
- Adversary: Avversario (in contesto cybersecurity, un attaccante)
- Lateral movement: Movimento laterale (spostamento all'interno di una rete dopo l'accesso)
- Defensive evasion: Evasione difensiva (técnica per eludere le difese di un sistema)
- Exfiltration: Espilazione (estrazione di dati sensibili da una rete)
- Tactic: Tattica (obiettivo tecnico specifico di un attacco)
- Mitigate: Mitigare (ridurre il rischio o l'impatto di un attacco)
Consigli per la pratica
Il video ha un tono formale e un ritmo moderato, ideale per esercitarti con la tecnica del shadowing. Ecco come procedere: prima, ascolta il video intero per capire il contesto. Poi, riproduci un frammento di 5-10 secondi e ripetilo immediatamente, cercando di imitare l'intonazione e la velocità. Usa un shadowing site per registrare la tua voce e confrontarla con l'originale: questo ti aiuterà a notare differenze nella pronuncia. Per la pratica di conversazione in inglese, riassumi i concetti del video in modo spontaneo, usando le parole chiave apprese. Ricorda: il shadow speech non è solo ripetere, ma capire e riprodurre il senso del discorso. Ripeti l'esercizio con sezioni più lunghe finché non senti che la sincronizzazione è naturale. Questo metodo migliorerà la tua fluenza e la tua capacità di comprendere discorsi tecnici in inglese.
Cos'è la tecnica dello Shadowing?
Shadowing è una tecnica di apprendimento delle lingue supportata da studi scientifici, originariamente sviluppata per la formazione dei traduttori professionisti e resa popolare dal poliglotta Dr. Alexander Arguelles. Il metodo è semplice ma potente: ascolti un audio in inglese di madrelingua e lo ripeti immediatamente ad alta voce — come un'ombra che segue il parlante con un ritardo di solo 1–2 secondi. A differenza dell'ascolto passivo o degli esercizi di grammatica, lo shadowing costringe il tuo cervello e i muscoli della bocca a elaborare e riprodurre simultaneamente i modelli di discorso reale. La ricerca dimostra che migliora significativamente la precisione della pronuncia, l'intonazione, il ritmo, il discorso connesso, la comprensione dell'ascolto e la fluidità del parlato — rendendolo uno dei metodi più efficaci per la preparazione alla prova di speaking dell'IELTS e per la comunicazione reale in inglese.