
ฝึกพูดภาษาอังกฤษด้วยเทคนิค Shadowing จากวิดีโอ: Firefox and Tor hit with 9.8 critical level exploit
 B2
A $6.3 billion open-weight model just got embarrassed by the French...
 C1
PostgreSQL in 100 Seconds
 C1
DNS Explained in 100 Seconds
 B2
Anthropic begged the world to stop AI… then shipped this
 B2
One man just liberated Fable... and now it’s illegal
 B2
7 Things No Programmer Ever Wants to Hear
 B2
80% of programmers are NOT happy… why?
 B2
Raspberry Pi Explained in 100 Seconds
 C1
Tragic mistake... Anthropic leaks Claude’s source code
 C1
100+ Docker Concepts you Need to Know
 C1
Docker in 100 Seconds
 C1
The mystery is solved... and the answer is 40x cheaper than Claude
 B2
An ex-OpenAI researcher just deleted language from the LLM...
 B2
25 crazy software bugs explained
 B2
Git Explained in 100 Seconds
 B2
There's a new Linux distro in town for developers...
 B2
The "vibe coding" mind virus explained…
 B2
Linux got wrecked by backdoor attack
 B2
7 Programming myths that waste your time
 C1
Nvidia CUDA in 100 Seconds
 B2
OpenAI’s new browser feels familiar…
 B2
I Outsmarted Pro Car Thieves
 B2
Windows Update Shouldn’t Be Allowed to Do This
 B2
The Internet Didn't Fail. It Was Taken.
 B2
Two Developers Before a Release: The Login Bug Is Back
 B2
How Ad Blockers Work
 C1
STOP Running Code On Your Computer
 B2
World's Deadliest Computer Virus: WannaCry
 B2
The Worst Sponsorships in YouTube History
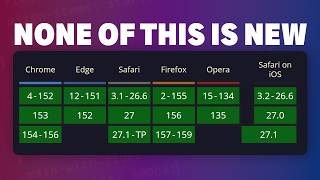 B2
Use these CSS features instead of JavaScript
 B2
The Gaming Market is Starting to Break.
คำศัพท์และข้อสังเกตด้านการพูดสำหรับบทเรียนนี้
บทเรียนฝึกพูดระดับ B2 นี้ใช้วิดีโอ “Firefox and Tor hit with 9.8 critical level exploit” เป็นสื่อ คำที่ถูกพูดซ้ำบ่อยที่สุด: code, browser, Firefox, pointer, animation วิดีโอนี้มี 47 ประโยค และ 991 คำ สำหรับฝึกพูดตาม ช่วงที่มีเสียงพูดยาว 4:27 ผู้พูดพูดเร็ว ประมาณ 223 คำต่อนาที จึงมีการเชื่อมเสียงและลดเสียงค่อนข้างมาก มีเพียง 80% ของคำที่อยู่ใน 3,000 คำที่ใช้บ่อยที่สุดในภาษาอังกฤษ คำศัพท์จึงค่อนข้างยาก
คำศัพท์สำคัญในวิดีโอนี้
คำที่ยากที่สุด 9 คำในวิดีโอ พร้อมคำอ่านและความหมาย:
| คำศัพท์ | คำอ่าน | ความหมาย |
|---|---|---|
| pointer คำนาม | /ˈpɔɪn.təɹ/ | ไม้ชี้ |
| animation คำนาม | /ˌæn.ɪˈmeɪ.ʃən/ | แอนิเมชัน |
| vulnerability คำนาม | /ˌvʌln(ə)ɹəˈbɪlɪti/ | ช่องโหว่ |
| bulletproof คำคุณศัพท์ | /ˈbʊlɪtpɹuf/ | กันกระสุน |
| analyze คำกริยา | /ˈæn.əˌlaɪz/ | วิเคราะห์ |
| scroll คำนาม | /skɹoʊl/ | ม้วนกระดาษ |
| vector คำนาม | /ˈvɛktɚ/ | เวกเตอร์ |
| mathematics คำนาม | /mæθ(.ə)ˈmæt.ɪks/ | คณิตศาสตร์ |
| garbage คำนาม | /ˈɡɑɹ.bɪd͡ʒ/ | กาก, ขยะ |
ไวยากรณ์ในวิดีโอนี้
โครงสร้างที่ผู้พูดใช้บ่อยที่สุด พร้อมคำพูดจริงจากวิดีโอ:
| โครงสร้าง | ในวิดีโอ |
|---|---|
| Passive voice be + กริยาช่อง 3 — เน้นสิ่งที่เกิดขึ้น ไม่ใช่ผู้กระทำ | were fired · has been credited · being written |
| Present perfect have/has + กริยาช่อง 3 — เหตุการณ์ในอดีตที่ยังเกี่ยวข้องกับปัจจุบัน | have tabled · has been credited · have affected |
| Relative clauses who / which + อนุประโยค — ข้อมูลเพิ่มเติมเกี่ยวกับคนหรือสิ่งของ | dangling, which is · Zen, which is |
การออกเสียงที่ควรระวัง
ผู้พูดใช้รูปย่อและรูปลดเสียง 13 ครั้ง เช่น you're, you'll, doesn't ให้พูดแบบสั้นตามที่ได้ยิน
- เสียง “sh” และ “zh”: animation /ˌæn.ɪˈmeɪ.ʃən/, malicious /məˈlɪʃəs/, subscription /səbˈskɹɪpʃən/
- คำยาว — ลงเสียงหนักให้ถูกพยางค์: animation /ˌæn.ɪˈmeɪ.ʃən/, vulnerability /ˌvʌln(ə)ɹəˈbɪlɪti/, interactive /ˌɪn.tɚˈæk.tɪv/, deallocate /diːˈæləkeɪt/, catastrophic /ˌkætəˈstɹɑfɪk/
เสียงที่คนไทยมักออกเสียงยาก:
- เสียงท้ายคำ — ออกเสียงให้ครบ ไม่เปลี่ยนเป็นตัวสะกดแบบไทย: dangle /ˈdæŋ.ɡəl/, interactive /ˌɪn.tɚˈæk.tɪv/, bulletproof /ˈbʊlɪtpɹuf/, ominous /ˈɑmɪnəs/, malicious /məˈlɪʃəs/
- /v/ — ไม่ใช่ /w/ ให้ฟันบนแตะริมฝีปากล่าง: vulnerability /ˌvʌln(ə)ɹəˈbɪlɪti/, interactive /ˌɪn.tɚˈæk.tɪv/, vector /ˈvɛktɚ/
- /z/ — เสียงก้อง ไม่ใช่ /s/: browser /ˈbɹaʊ.zəɹ/, analyze /ˈæn.əˌlaɪz/
วิธีฝึกกับวิดีโอนี้
- ฟังวิดีโอให้จบหนึ่งรอบโดยยังไม่ต้องพูด แล้วจดคำที่ยังไม่รู้จัก
- เริ่มที่ความเร็ว 0.75× พูดตามทีละประโยค แล้วกลับไปใช้ความเร็วปกติเมื่อเริ่มคล่อง
- อัดเสียงตัวเองแล้วเทียบกับต้นฉบับ โดยสังเกตคำอย่าง pointer, animation, vulnerability เป็นพิเศษ
เทคนิค Shadowing คืออะไร?
Shadowing เป็นเทคนิคการเรียนรู้ภาษาที่ได้รับการรับรองทางวิทยาศาสตร์ พัฒนาขึ้นสำหรับการฝึกนักแปลมืออาชีพ วิธีการนี้เรียบง่ายแต่ทรงพลัง: คุณฟังเสียงภาษาอังกฤษจากเจ้าของภาษาและพูดตามทันที — เหมือนเงาที่ตามผู้พูดด้วยช่วงเวลาห่าง 1-2 วินาที การวิจัยแสดงว่าเทคนิคนี้ปรับปรุงความแม่นยำในการออกเสียง ทำนองเสียง จังหวะ การเชื่อมเสียง การฟังเข้าใจ และความคล่องแคล่วในการพูดได้อย่างมีนัยสำคัญ